Cybersecurity Insights & Expertise
Stay ahead of evolving threats with expert analysis, industry trends, and practical cybersecurity guidance from our team of security professionals.
Featured Article
 Featured
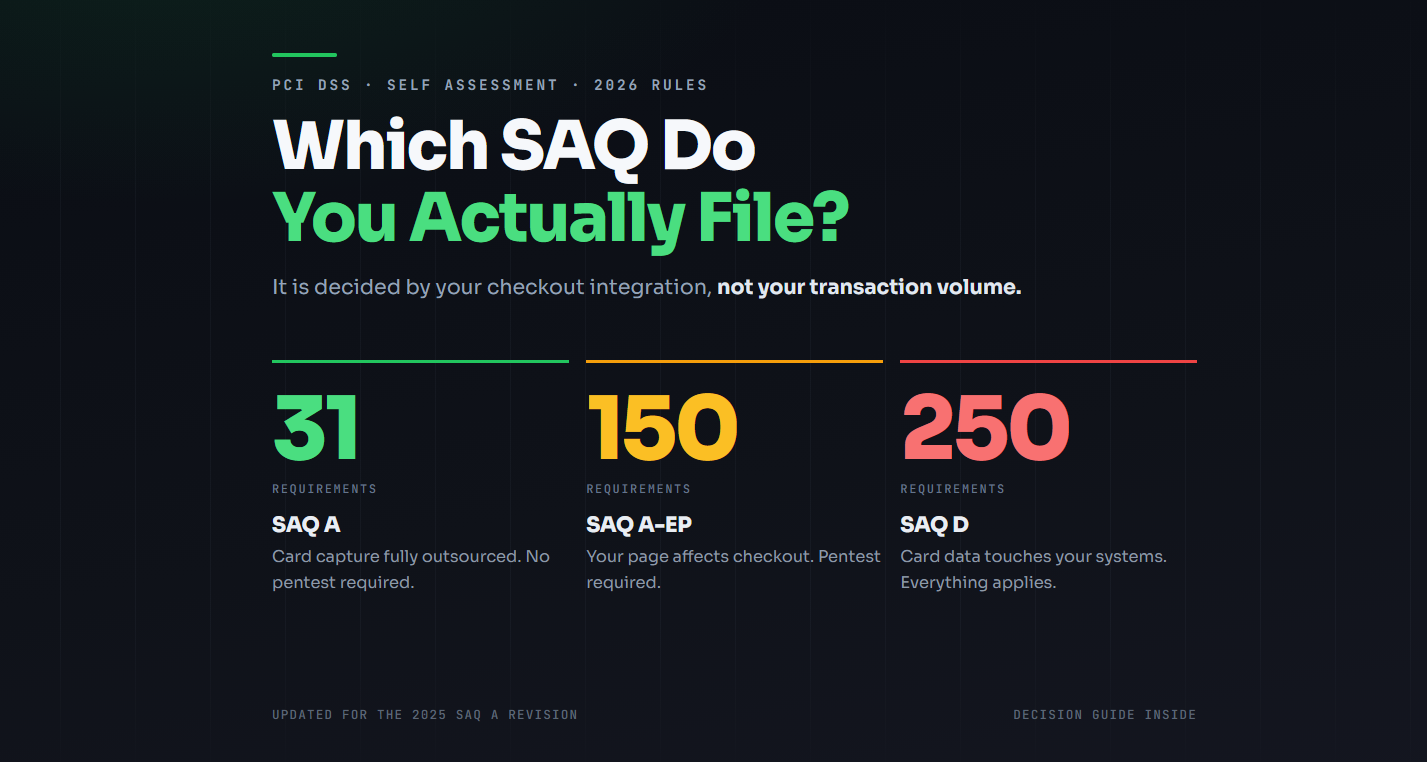
SAQ A vs SAQ A-EP vs SAQ D: Which One Applies to You
Quick answer SAQ A is for merchants who have fully outsourced card capture. Every element of the payment page comes directly from your provider, and card data never reaches a system you control. Around 31 requirements. SAQ A-EP is for e-commerce merchants whose own website affects the payment page but never receives card data. Your page loads the provider's script, redirects, or controls the form. Around 150 requirements, roughly five times the work. SAQ D is the catch-all. If card data tou
Muhammad Khizer Javed
Oct 9, 2026
Latest Articles
Showing 1-12 of 99 articles
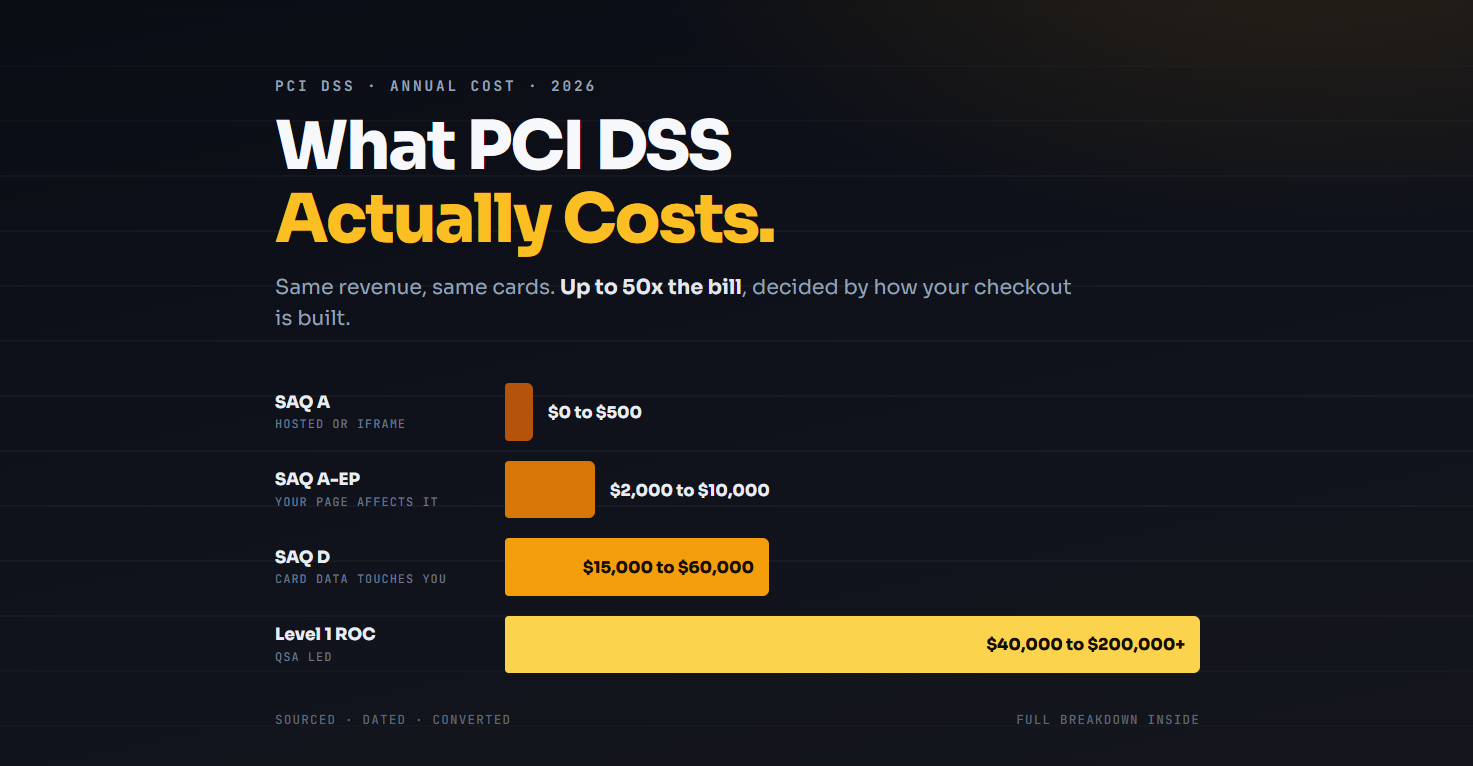
PCI DSS Compliance Cost in 2027: Real Price Breakdown
Quick answer PCI DSS compliance costs between about $500 and $200,000 a year, and the single biggest factor is not your company size. It is how your checkout is built. A merchant whose payment page is a hosted iframe from Stripe or Adyen files SAQ A and pays a few hundred dollars a year. The same business processing the same volume through a server-side API integration files SAQ D and pays tens of thousands. Same revenue, same cards, roughly 50 times the compliance bill, decided by an archit
Muhammad Khizer Javed
Oct 9, 2026
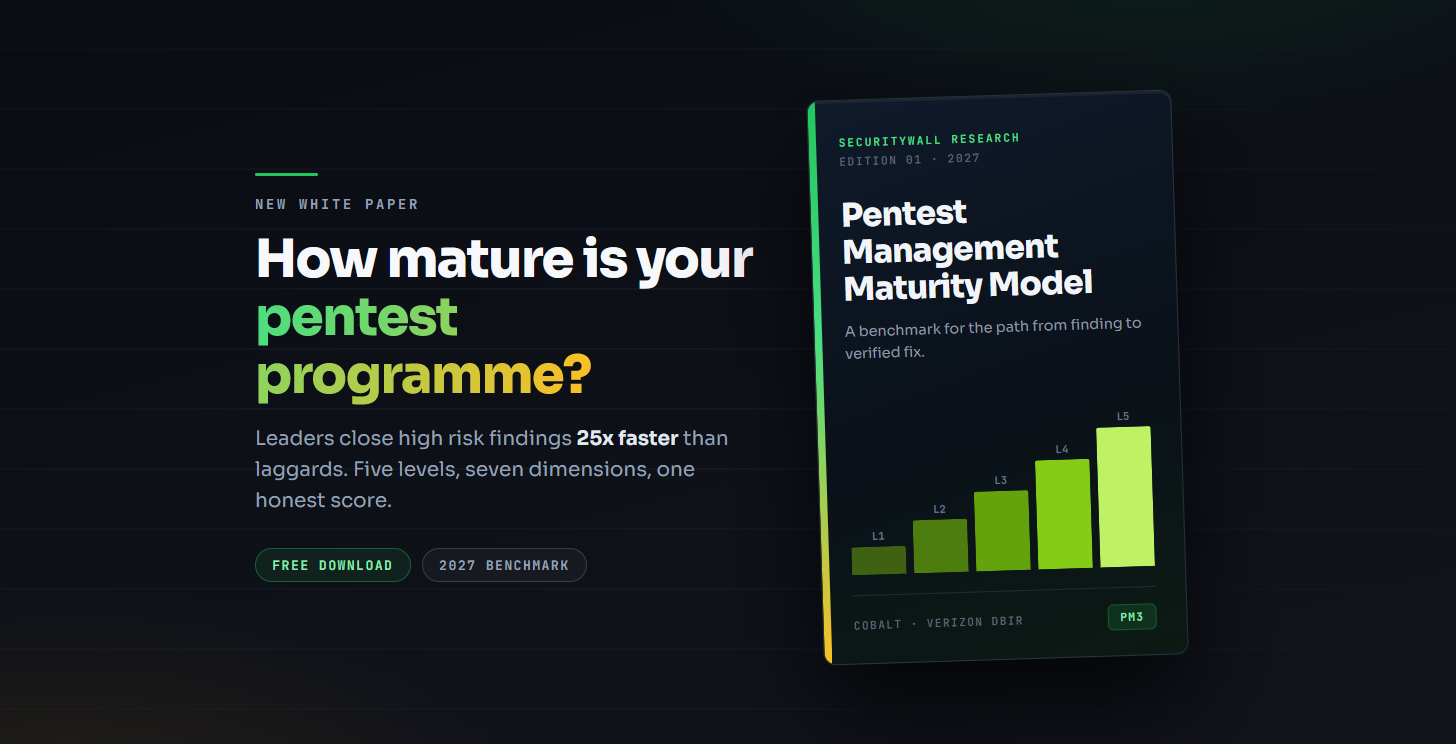
Pentest Management Maturity Model White Paper: 2027 Benchmark
Disclosure PM3 is an open framework, published by SecurityWall and free to use, cite, adapt and build on. No licence, no certification body, no fee. Consultancies are welcome to score clients with it, GRC teams to benchmark against it, and other vendors to map their products to its levels. We would rather the category had a shared vocabulary for remediation maturity than keep one to ourselves. We built it because our clients kept asking the same question and the industry had no answer: how
Hisham Mir
Oct 9, 2026
SLASH vs PlexTrac: Pentest Management Compared
Disclosure before you read SecurityWall builds SLASH. This page compares our product to a competitor, so read it with that in mind. We have put "Where PlexTrac wins" before "Where SLASH wins", named seven specific areas where PlexTrac is the better choice, and told you plainly which team should buy which. If you want a neutral starting point instead, our roundup of PlexTrac alternatives covers six platforms including both of these. The short verdict PlexTrac is the incumbent. SLASH is the h
Muhammad Khizer Javed
Oct 1, 2026
PlexTrac Alternatives: 6 Platforms Compared
Disclosure before you read SecurityWall builds SLASH, one of the platforms below. We have reviewed it on the same criteria as everything else and named the three situations where you should buy something other than SLASH. Every price is sourced and dated, including the gaps. Quick answer Most lists of PlexTrac alternatives compare products that are not alternatives. Ghostwriter and SysReptor are report generators. They turn notes into a PDF. They do not track remediation, do not sync ticket
Babar Khan Akhunzada
Oct 1, 2026
Penetration Testing Cost FAQ: SOC 2, ISO 27001, PCI DSS
Seven questions buyers ask right before booking Every answer below is direct and self contained. Ranges are market rates from published sources, listed under each answer. SecurityWall quotes fixed scope in a call rather than posting a price list, so treat these as budget planning bands, not quotes. 01What does a penetration test cost, generally? 02API security assessment for about 50 endpoints? 03LLM or chatbot penetration test cost? 04PCI DSS pentest: what to ask vendors for? 05Will my audi
Babar Khan Akhunzada
Aug 24, 2026
ISO 27001 & SOC 2 Penetration Testing: What Auditors Want
QUICK ANSWER · BOTH FRAMEWORKS AUDIT EVIDENCE · 2026 Does ISO 27001 require a penetration test? Not by name. ISO/IEC 27001:2022 is risk based, but Annex A 8.8 (management of technical vulnerabilities) and Annex A 8.29 (security testing in development and acceptance) are the applicable controls, and ISO/IEC 27002:2022 names penetration testing in its implementation guidance. If those controls are marked applicable in your Statement of Applicability and you cannot show test evidence, that is a
Hisham Mir
Aug 24, 2026
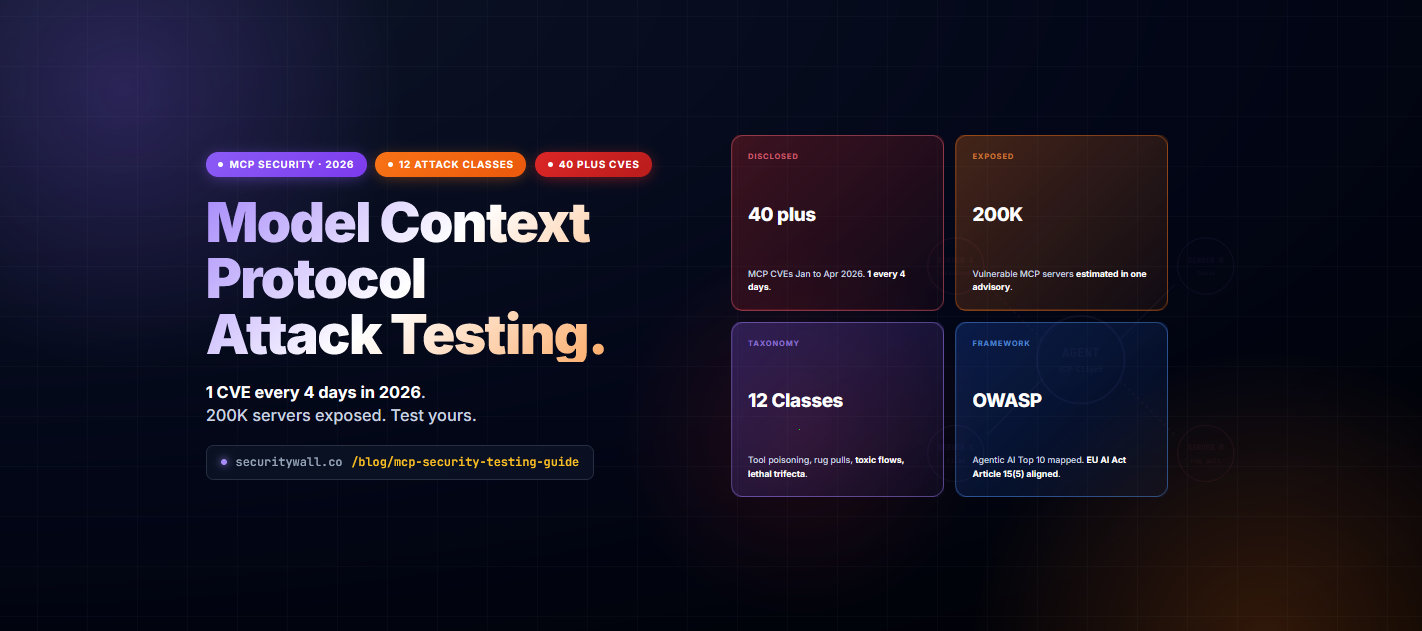
MCP Security Testing 2026: Model Context Protocol Risks
× Running MCP servers in production? 40 plus CVEs in 2026 · Are you exposed? Schedule a Meeting → QUICK ANSWER · MCP SECURITY 40 PLUS CVES · 2026 The Model Context Protocol (MCP), released by Anthropic in November 2024, lets AI agents call external tools, APIs, files, and services through a standardised interface. Between January and April 2026, security researchers disclosed more than 40 CVEs against MCP implementations across Python, TypeScript, Java, and Rust SDKs. Estimated 200,000 MCP se
Hisham Mir
Aug 4, 2026
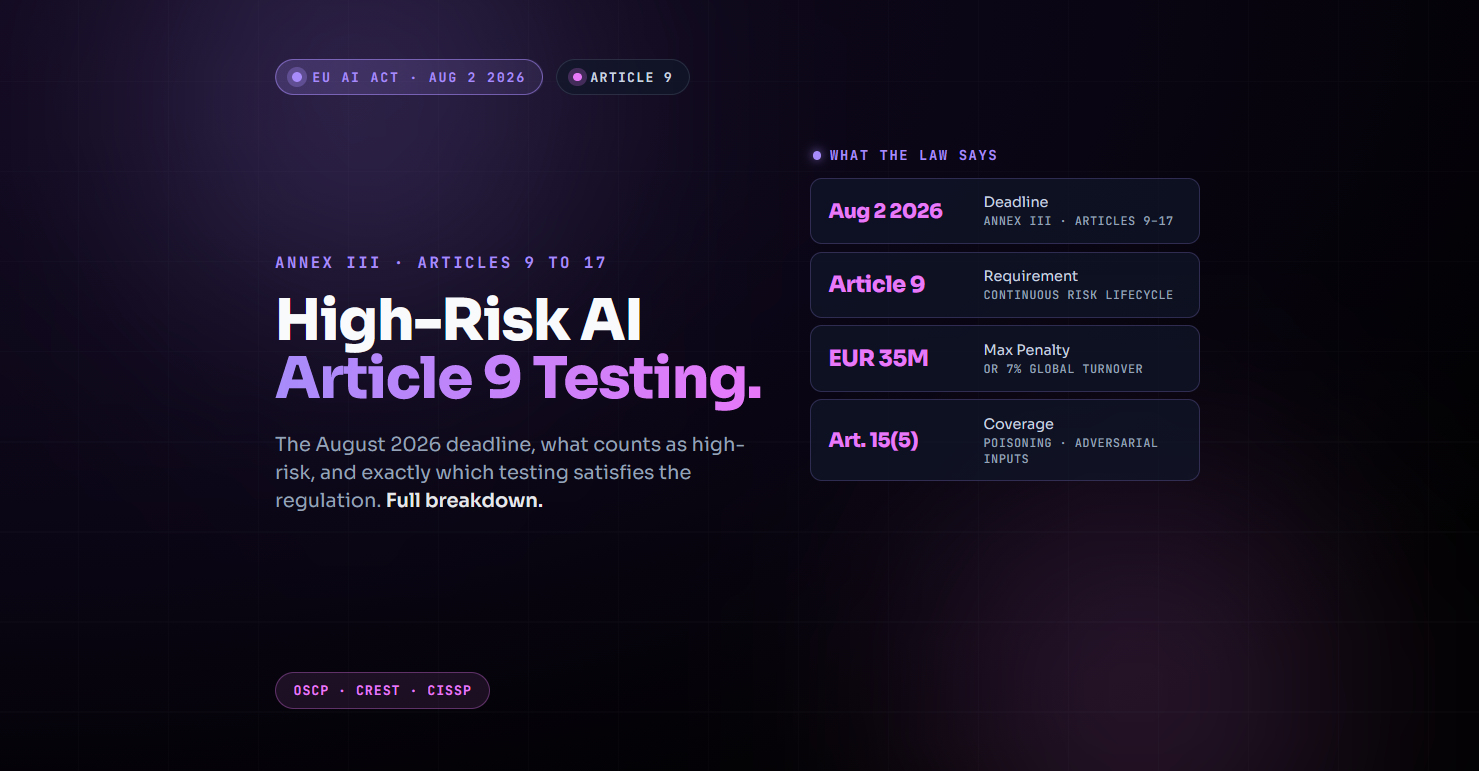
EU AI Act Security Testing: What Article 9 Requires
× August 2026 high risk AI deadline? Article 9 security testing · Ready? Schedule a Meeting → QUICK ANSWER · EU AI ACT AUG 2 2026 DEADLINE EU AI Act Regulation 2024/1689 Article 9 requires providers of high risk AI systems to establish, implement, document, and maintain a risk management system throughout the AI system lifecycle. The Act explicitly names security testing as a required control: Article 9(6) mandates testing before market placement and throughout development, Article 9(8) requi
Babar Khan Akhunzada
Jul 23, 2026
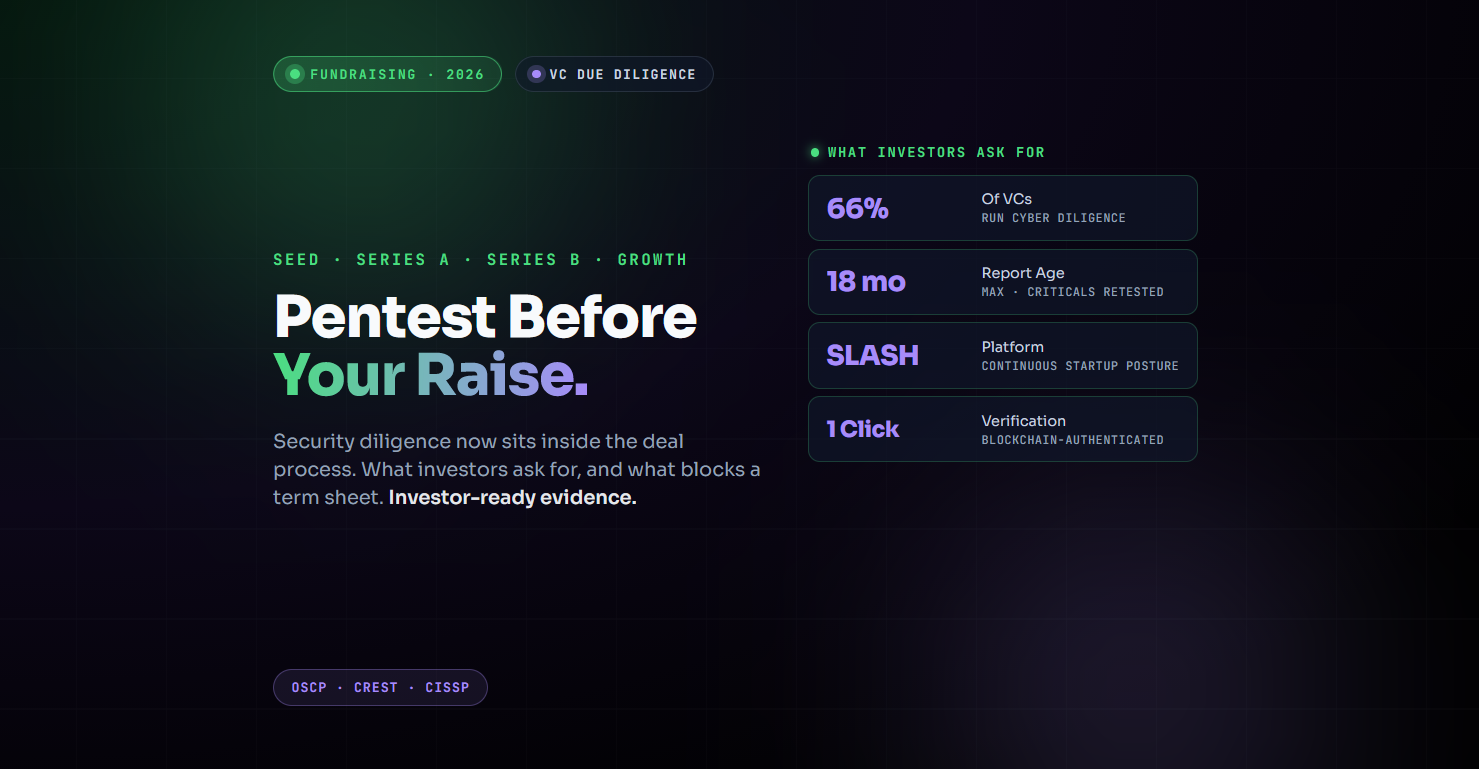
Penetration Testing Before Fundraising: What VCs Require
× Raising? Investors ask about security. Pentest for VC diligence · 2 to 3 weeks Schedule a Meeting → QUICK ANSWER · FUNDRAISING SECURITY DEAL BLOCKER · 2026 A penetration test before fundraising is a scoped security assessment run in the weeks before a Series A, B, or growth round to produce the evidence a VC's technical due diligence team will ask for. In 2026 approximately 66% of VCs now conduct cybersecurity due diligence before funding, and Verizon's 2026 DBIR finds 31% of breaches now s
Hisham Mir
Jul 23, 2026
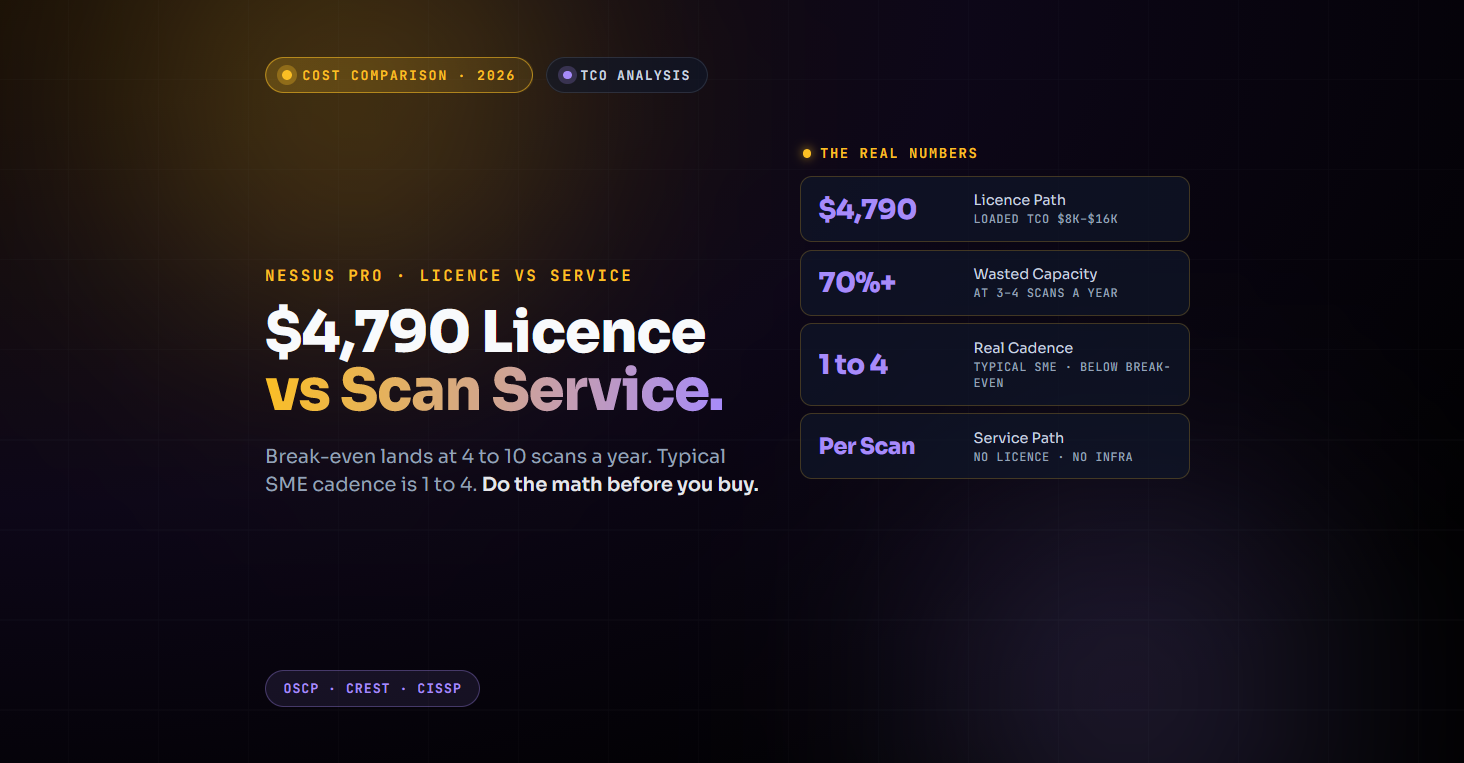
Buying a Nessus Licence vs Scan Service: Cost Comparison
× Scan a few times a year? Skip the $4,790 licence · SME friendly quote Schedule a Cost Comparison Call → QUICK ANSWER · COST COMPARISON TCO ANALYSIS · 2026 Tenable Nessus Professional costs $4,790 per year for a single scanner with unlimited target IPs (Tenable published pricing, verified July 2026). Real total cost of ownership including scanner infrastructure, analyst time to interpret findings, compliance framework mapping, and reporting typically runs $8,000 to $15,000 in year one for an
Muhammad Khizer Javed
Jul 22, 2026
Nipper Firewall Audit Cost 2026: What You Actually Pay
× Small fleet, need real audit? Router, switch, firewall config audit · SME friendly Schedule a Scoping Meeting → QUICK ANSWER · NETWORK AUDIT PRICING TRANSPARENCY · 2026 Titania Nipper is a network configuration audit tool used by 30+ US federal agencies and 800+ organisations globally to assess firewalls, routers, and switches against CIS Benchmarks, NIST 800-53, PCI DSS, CMMC, STIGs, and other frameworks. Titania does not publish official pricing. Market intelligence from Gartner Peer In
Hamza Razzaq
Jul 21, 2026
API Security Assessment for Partner Integrations
× Integration blocked by security? API pentest with OWASP mapping · 2 week delivery Get an API Security Scoping Call → QUICK ANSWER · API INTEGRATION LAUNCH BLOCKER · 2026 An API security assessment for a partner integration is a scoped penetration test of the specific API surface your integration exposes, mapped to OWASP API Security Top 10 (2023), the partner platform's own security requirements, and any regulatory frameworks that apply (PCI DSS, GDPR, SOC 2). It covers authentication and
Babar Khan Akhunzada
Jul 21, 2026